
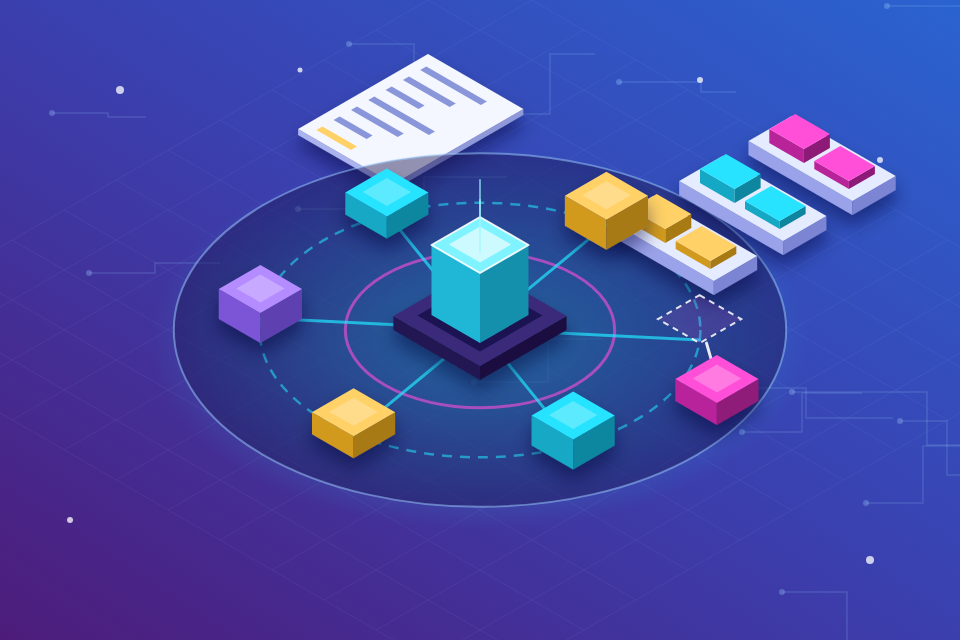
env zero, which sells cloud governance and Infrastructure as Code (IaC) orchestration, announced the Early Access launch of EZ Control on September 29 at DevOpsCon & AI Platform Engineering Day in New York. The company calls it an autonomous cloud control plane: software that detects when a cloud environment has diverged from what the enterprise intended, decides the right response under policy, and carries out the fix itself.
The premise is that IaC only describes what teams meant to deploy. Changes made by hand in a console, break-glass fixes, automated pipelines and increasingly AI agents provisioning infrastructure create resources that IaC tools never see, and env zero argues the review process built for human-paced change cannot keep up. Its criticism of the market is that the usual answer has been more detection, another dashboard or alert queue, which leaves the harder work of deciding what to do and doing it safely to an engineer who has to rebuild ownership, blast radius and policy context by hand.
One inventory, one ontology
EZ Control builds on the March 2026 merger of env zero and CloudQuery. It discovers cloud and SaaS resources through more than 80 integrations, reconciles what is running against what code declared, and structures the result into a single context layer. env zero says the inventory covers nearly 2,300 resource types across Amazon Web Services, Microsoft Azure, Google Cloud Platform and Kubernetes, and contrasts that with inventory tools built around a few dozen popular services.
That inventory feeds what the company calls a continuously synced ontology. Each resource is linked to the code that declared it, the team that owns it, its cost, its dependencies, the policies that apply to it and the risks attached to it. env zero’s argument is that this is what makes autonomous action safe, because the system does not need a human to assemble the picture before acting.
Drift is one gap among several
EZ Control ingests policy from wherever an enterprise already keeps it, including IaC, cloud security posture management tools, policy-as-code repositories and cloud-provider guardrails, and enforces it against the same ontology. A resource that has drifted from its module, a database that has fallen out of a compliance benchmark, an instance oversized against a cost policy, a cluster overdue for patching and a workload outside its availability requirements are treated as one problem: a gap between intended and actual state with an owner, a policy and a remediation path. Security, availability, maintenance, cost and performance are handled in a single loop rather than five separate tools.
Autonomy set by policy
Customers choose how far EZ Control may go for each class of resource: observe only, propose a fix, act with approval, or act autonomously within defined guardrails. Within those limits, the company says it corrects unintentional drift by reapplying IaC, records intentional changes as a pull request against the owning repository, and flags defects in source code. For violations of a security, cost, availability, maintenance or performance policy, it applies the remediation the owning policy defines. Every action follows the repository and review process that owns the resource, and a post-fix scan verifies the issue is closed.
The same path applies to software agents. Because every change runs through EZ Control, env zero says the policies, approvals and audit trail that govern human engineers also govern AI agents, which therefore do not need raw cloud credentials.
"The cloud is already being changed autonomously, by pipelines, by automation and now by AI agents. What is missing is a control plane that can respond at the same speed, inside the guardrails the enterprise has already set," said Steve Corndell, CEO of env zero. "Autonomy is only ever as trustworthy as the context underneath it. That is what lets EZ Control act rather than alert, under policy, with a named owner and a complete audit trail."
Roy Illsley, Chief Analyst at Omdia, said enterprises need trusted context that explains what changed, who owns it, the business impact and how to remediate safely, and that by bringing discovered and declared state together EZ Control "has the potential" to help platform teams shorten the path from spotting a cloud issue to a governed, verifiable resolution. His comment is hedged, as is usual for an analyst quote in a vendor release, and it stops short of judging the product.
Availability
EZ Control is offered through an Early Access program and is delivered as SaaS. The initial connection is agentless and read-only, which is the observe-only level, so organizations can find resources and governance gaps before granting it authority to act; autonomy can then be raised one resource class at a time. Prospective participants can register at envzero.com. The announcement does not give pricing or a general availability date.
What to ask before granting write access
The coverage figure, the 80-plus integrations and the claim of reversible, auditable action are all env zero’s own, and the release names no customers. It does not say how the system handles conflicting policies from different sources, what happens when a remediation fails partway, or how rollback works across resource types. The read-only starting point is the sensible way to test those points: teams can see what EZ Control finds in their own estate before deciding how far up the autonomy ladder to go.
Leave a Reply