
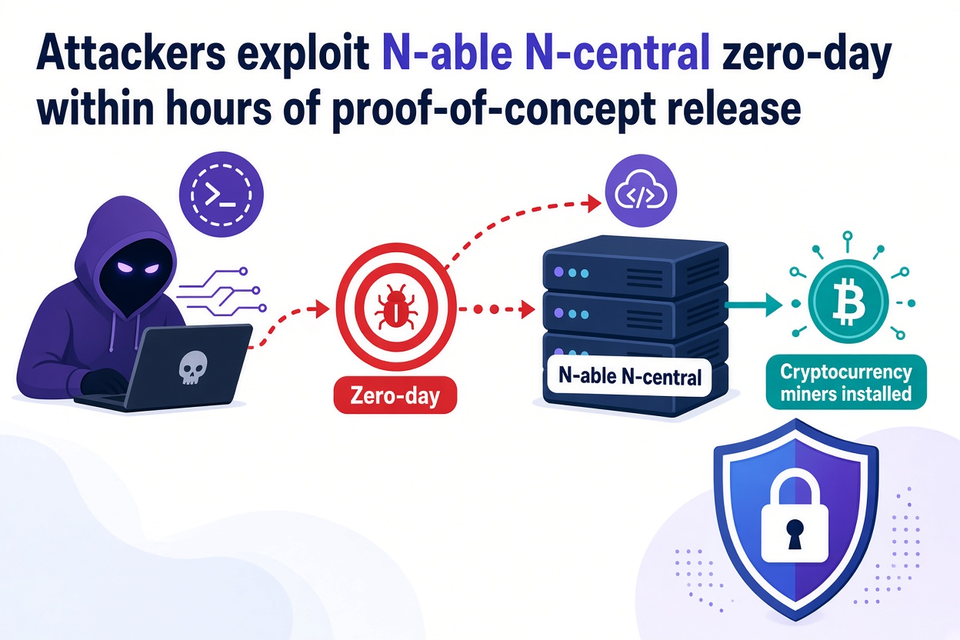
Attackers are breaking into N-able N-central servers through a newly disclosed zero-day vulnerability and installing cryptocurrency miners on them, BleepingComputer reports. Researchers put the count at 21 affected systems at minimum. Nineteen of those were running the company's latest security update.
That ratio matters more than the total. A zero-day is a flaw that attackers use before a working fix reaches the people running the software, and 19 of 21 systems on the current update would suggest that patching to the latest release did not, by itself, keep a server off the list. The count is also a floor. How many more servers are affected is unknown.
Hours from code to compromise
Named "4EverAble2Shell," the vulnerability moved from disclosure to live attacks quickly. BleepingComputer reports that exploitation began hours after the release of a proof-of-concept, meaning working code that shows how to trigger the flaw. Published exploit code shortens the distance between a researcher's write-up and a usable attack, and here the gap was measured in hours.
The payload so far is cryptocurrency mining software, which uses a compromised machine's processors to generate digital currency for whoever planted it. For an operator, that means compute and electricity spent on someone else's account. It also means an outsider has shown the ability to run code on the server, which is the larger problem.
Operators of N-central servers cannot treat patch level as proof of safety on this evidence. If the 19-of-21 pattern holds as more cases surface, checking for unexpected mining processes and unexplained processor load would tell an administrator more than a version number would.
Leave a Reply